Wazuh
Open-source SIEM/XDR: log analysis, intrusion and vulnerability detection.
Open source Cloud + desktop
- Platforms
- Linux server; agents for Windows/Linux/macOS; web; cloud
- Licence
- Open source — GPLv2
- Price
- Free (self-hosted); paid Cloud
- Updated
- 2026-11-05
What it is
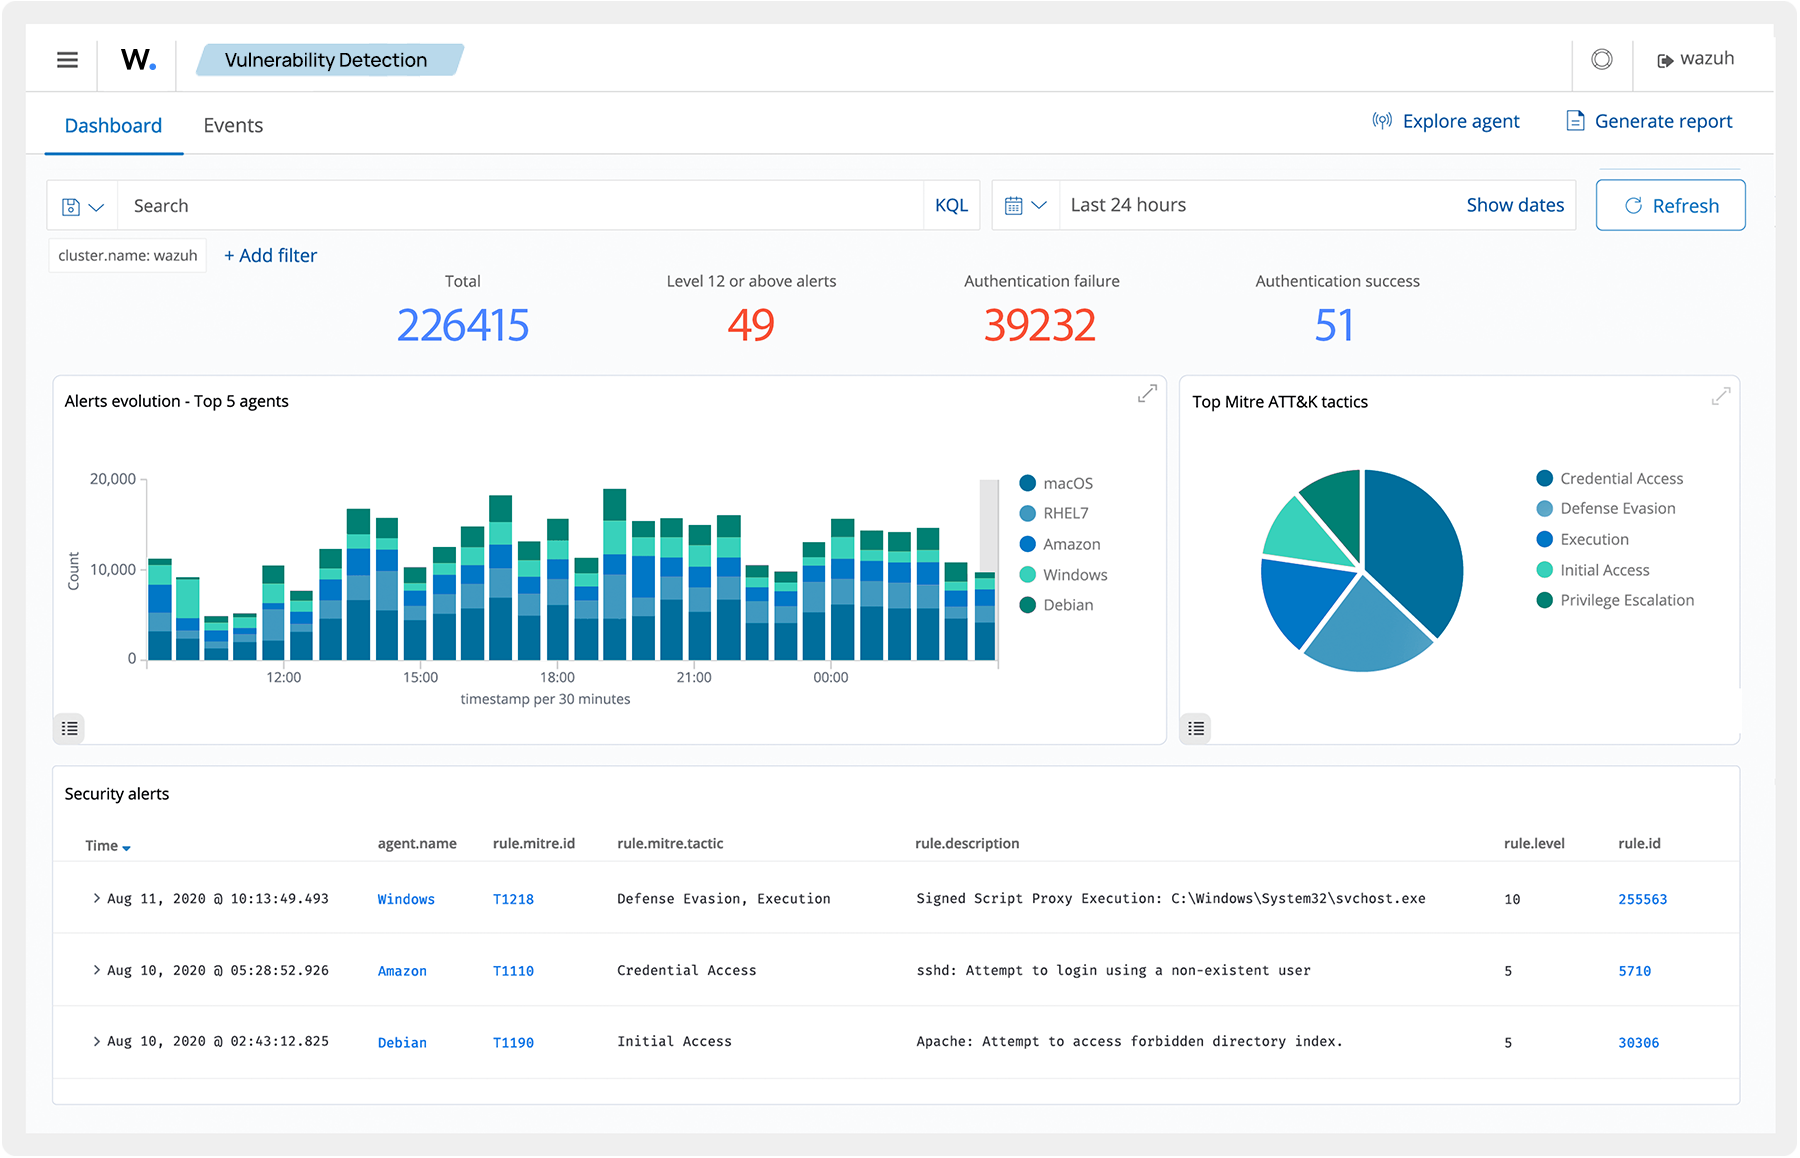
Wazuh is an open-source SIEM/XDR platform: security monitoring, log collection and analysis, intrusion detection and vulnerability checks. It watches events across machines, verifies file integrity and supports compliance (PCI DSS, HIPAA) — a free alternative to Splunk.
Problems it removes
- You want SIEM/XDR capability without Splunk-level licensing cost.
- Logs and detections from every host need centralising and correlating.
- Compliance (PCI DSS, HIPAA) requires file-integrity and policy checks.
How administrators use it
- Deploy agents to send logs and events to the Wazuh server.
- Use the dashboard for detections, file-integrity monitoring and vulnerability data.
- Map alerts to compliance requirements.
Strengths & trade-offs
Strengths
- Free and open source (self-hosted).
- SIEM, XDR, file-integrity and vulnerability detection in one.
- Built-in compliance mappings.
Trade-offs
- You run and scale the stack yourself.
- Tuning rules to cut noise takes effort.
Common questions
Is Wazuh free?
Yes, self-hosted and open source. A paid managed Cloud offering also exists.
Is it a Splunk alternative?
For many SIEM use cases, yes — a free, open alternative, though Splunk’s ecosystem is larger.